A Pattern Spreading Faster Than Defences
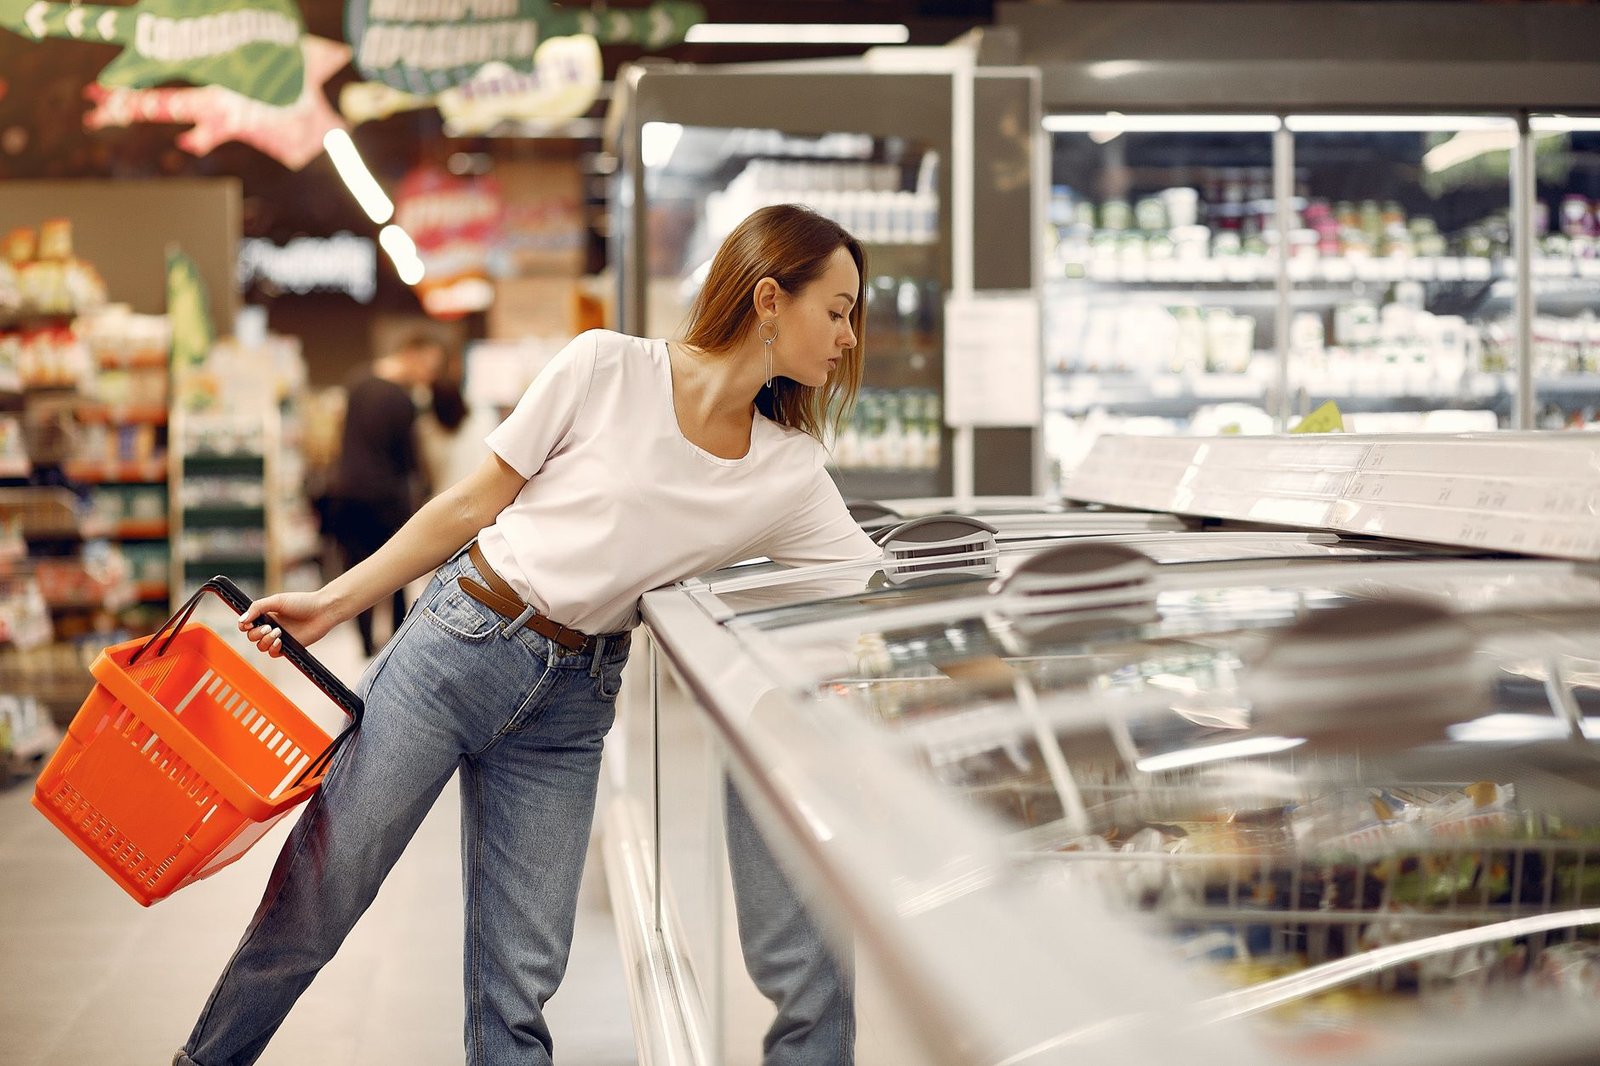
Overnight on a Monday, supermarket chains in at least seven European countries woke up to a problem nobody wants to find in their stockroom. Refrigerators and freezers in some stores had been pushed to temperatures as high as 50C, or 122F. Retailers in Belgium, Estonia, Ireland, Finland, Luxembourg, the Netherlands and Sweden reported failures, and several confirmed they had been hacked. The episode followed a similar attack in France the previous month, where hackers reportedly seized control of cooling units in as many as 700 supermarkets, causing fires and food losses estimated in the tens of millions of euros.
What makes these incidents unsettling is their simplicity. Nobody demanded a ransom. There was no obvious financial motive, no leaked database, no extortion note. Security researchers quoted in the coverage described something closer to sabotage: a few commands sent to a temperature controller can spoil thousands of euros of stock and shut a store within hours. The EU food and agriculture commissioner called the attacks a deliberate attempt to disrupt the food supply chain and erode consumer confidence, and that framing is hard to dismiss.
Why Cooling Systems Make Such Soft Targets
Modern refrigeration is no longer a simple box with a thermostat. Large retail chains run vast networks of connected controllers, building management systems and door sensors, many of which can be monitored and adjusted remotely. That convenience is valuable for maintenance teams, but every remotely reachable device is also a potential entry point. Researchers noted that thousands of these controllers were still reachable from the internet after the French attack, and that some carried known security flaws that had not been patched. The manufacturer of the controllers involved in France said it had identified vulnerabilities the previous year and had long recommended that customers install updates. The gap between a fix being available and a fix being applied is where attackers operate.
Swedish authorities said the country had a considerable number of exposed operational technology devices needing updates, a finding that probably applies well beyond Sweden. Operational technology, the hardware that runs physical processes, was rarely designed with internet exposure in mind, and many organisations still manage it with the patching habits of an office IT department, if at all. Given that European officials are openly worried about state-linked hybrid operations since Russia’s invasion of Ukraine, the question is no longer whether attackers will find these weak points, but how quickly operators can close them.
What This Means for Shoppers and the Connected Home
For most people, the immediate impact was empty shelves and apologetic signs rather than dramatic harm, but the wider lesson reaches into homes and kitchens. Consumers are buying Wi-Fi-enabled fridges, freezers, thermostats and smart plugs in growing numbers, often on the strength of convenience features like remote temperature alerts and app control. Purchase decisions increasingly weigh connectivity as a selling point, yet security support, update commitments and the length of firmware maintenance rarely appear on the box. Shoppers researching a new appliance should look for stated update policies, clear privacy documentation and a manufacturer that publishes security advisories. When intent to buy a connected appliance is high, so is the value of asking those questions before checkout rather than after the first unexplained alert.